

The worst thing that ever happened to privacy and healthcare? HIPAA and the overturn of Roe v. Wade. The law of unintended consequences is perhaps the only law our current Supreme Court is interested in upholding the prescient of! The right to an abortion was based on the court’s enumeration of a federal right to privacy.
This article is about what happens when that right to privacy is abruptly pulled away, like the bottom block of a Jenga puzzle, leaving us with nonsensical regulation. HIPAA is now a bad law. This is not just because it is a wildly misspelled acronym1 on the regular. It’s because it’s a law that— absent federal regulation about what privacy must be respected by state and local governments —creates a backdoor into personal information for over-ambitious state lawmakers, while still getting in the way of meaningful communication in healthcare. This is especially true as it relates to the care of psychiatric patients, in the most vulnerable conditions.
I’d like to Enumerate the World a Coke
I am really thirsty. I’d like a Coke. Were I to be prevented from purchasing a Coca-Cola from a vending machine, I could, assuming I was extremely litigious, file a lawsuit.
Let’s say the vending machine is magic and there is no way in which it has any interaction with interstate commerce. It is in the same state as Coke is manufactured. It is not hooked up to the Internet. Nothing.
I have a right to have my thirst quenched. Yes, I know you don’t see the cool satisfaction of a Coke on a hot day in the constitution. There is no legal review necessary to drink a Coke. This is an example of a right enumerated to the states or to me as an individual by the constitution.2
Now, join me for an insane thought experiment: I am going to be a public health zealot, and pass a law that permits me to put to death any individual with an abrupt spike in blood sugar as a result of drinking a Coca-Cola.
To make it even more punitive, any abrupt spike in blood sugar will be presumed to be due to the delicious and thirst quenching— but, regrettably, sugar soaked beverage—and that blood glucose level in the medical record will also be evidence used to put an individual to death for the violation of the No Refreshing Coke Act of 2022. In the state of New York, you can bet that previous administrations would have gone to this length if only they were allowed.3
This sounds insane. But this is actually the situation we are now in, here in America4. No one wants to be put to death for getting their thirst quenched…but, it’s what’s happening. This brings us to the most misunderstood law in healthcare, which we presume has something to do with privacy, and we even more frequently misspell:
The Health Insurance Portability and Accountability Act: HIPAA
In 1996, HIPAA was passed into a federal law. It allowed for both the protections of personal health information and the disclosure of that same personal health information by covered entities. This does not include everyone. This is really really really really really important.
The following groups are considered covered entities under HIPAA, a.k.a. they have to comply with this federal law:
Healthcare providers: Every healthcare provider, regardless of size of practice, who electronically transmits health information in connection with certain transactions. These transactions include:
Claims
Benefit eligibility inquiries
Referral authorization requests
Other transactions for which HHS has established standards under the HIPAA Transactions Rule.
You’re gonna notice something really specific about the above. It applies to all healthcare providers who process transactions by claims. That is not all transactions. It’s just transactions that interface with traditional health insurance through benefit eligibility inquiries, authorization requests, and other HIPAA transactions. It doesn’t mean everybody.
If you have a medical or therapy practice and you take no insurance whatsoever, you never check benefits eligibility, you only ever get paid in ways that are not specified by HIPAA—cash only, for example, you would not be considered a HIPAA covered entity.
And that means the entirety of the law, including the protections around “protected5 health information” and the requirements for others to be able to access that information do not apply to this practice. They do not apply to your patients. They do not apply to your health technology. They do not apply to your medical records. If you sign up for a health record that is HIPAA compliant, you’re doing it wrong. That means it’s not private. That means it’s got a giant back door! Now in all practicality, there was almost no reason for anyone previously to engineer non-compliant solutions.
Until now…let’s take a look at why: The following are also considered covered entities:
Health plans:
Health plans include:
Health, dental, vision, and prescription drug insurers
Health maintenance organizations (HMOs)
Medicare, Medicaid, Medicare+Choice, and Medicare supplement insurers
Long-term care insurers (excluding nursing home fixed-indemnity policies)
Employer-sponsored group health plans6
Government- and church-sponsored health plans
Multi-employer health plans
Let’s figure out what the full scope of covered entities looks like:
Healthcare clearinghouses: Entities that process nonstandard information they receive from another entity into a standard (i.e., standard format or data content), or vice versa.
Business associates: A person or organization (other than a member of a covered entity’s workforce) using or disclosing individually identifiable health information to perform or provide functions, activities, or services for a covered entity. These functions, activities, or services include:
Claims processing
Data analysis
Utilization review
Billing
And a careful reading of the above makes it pretty clear that business associates covered by business associate agreements only have to comply with HIPAA if they’re performing services for a covered entity.
So, to summarize: HIPAA is a law that applies to those healthcare practices that are processing claims electronically. If you’re a 100% cash pay private practice and don’t interact with insurance in a way that processes claims—it’s not a law that applies to you.
I’m Going to Tell all of Your Secrets
But why would we ever want to not comply with it? Isn’t privacy important? Of course it is. But here is the really broken part of that law: It allows for the punishment of violations by individuals working with covered entities, but it also allows for the disclosure of information without the consent of the person when:
The law permits, but does not require, a covered entity to use and disclose PHI, without an individual’s authorization, for the following purposes or situations
(I am taking out all the sections that make any actual sense and putting them in the footnote7 and just fast forwarding to the egregious violations of privacy that make me want to take a shower):
The “Privacy Rule” permits disclosure of PHI, without an individual’s authorization or permission, for 12 national priority purposes:
When required by law
Public health activities
Victims of abuse or neglect or domestic violence
Health oversight activities
Judicial and administrative proceedings
Law enforcement
Functions (such as identification) concerning deceased persons
Cadaveric organ, eye, or tissue donation
Research, under certain conditions
To prevent or lessen a serious threat to health or safety
Essential government functions
Workers’ compensation
I want you to take a deep breath, and understand that what the above law allows is a massive government back door into our personal health information when they deem it necessary. So any state can pass any law in the absence of a federal right to privacy in which they now have a government interest in law-enforcement of. And if there is no limit on the laws they can pass that invade our privacy, literally any law passed can allow the government to access our health information.
Not only can they kill you for having your blood sugar spike, but they can invade your medical record to make sure they know when your blood pressure spikes so they know when to kill you. Yes, I know this sounds like hyperbole. But then I see this headline the very morning I am finishing off this article:
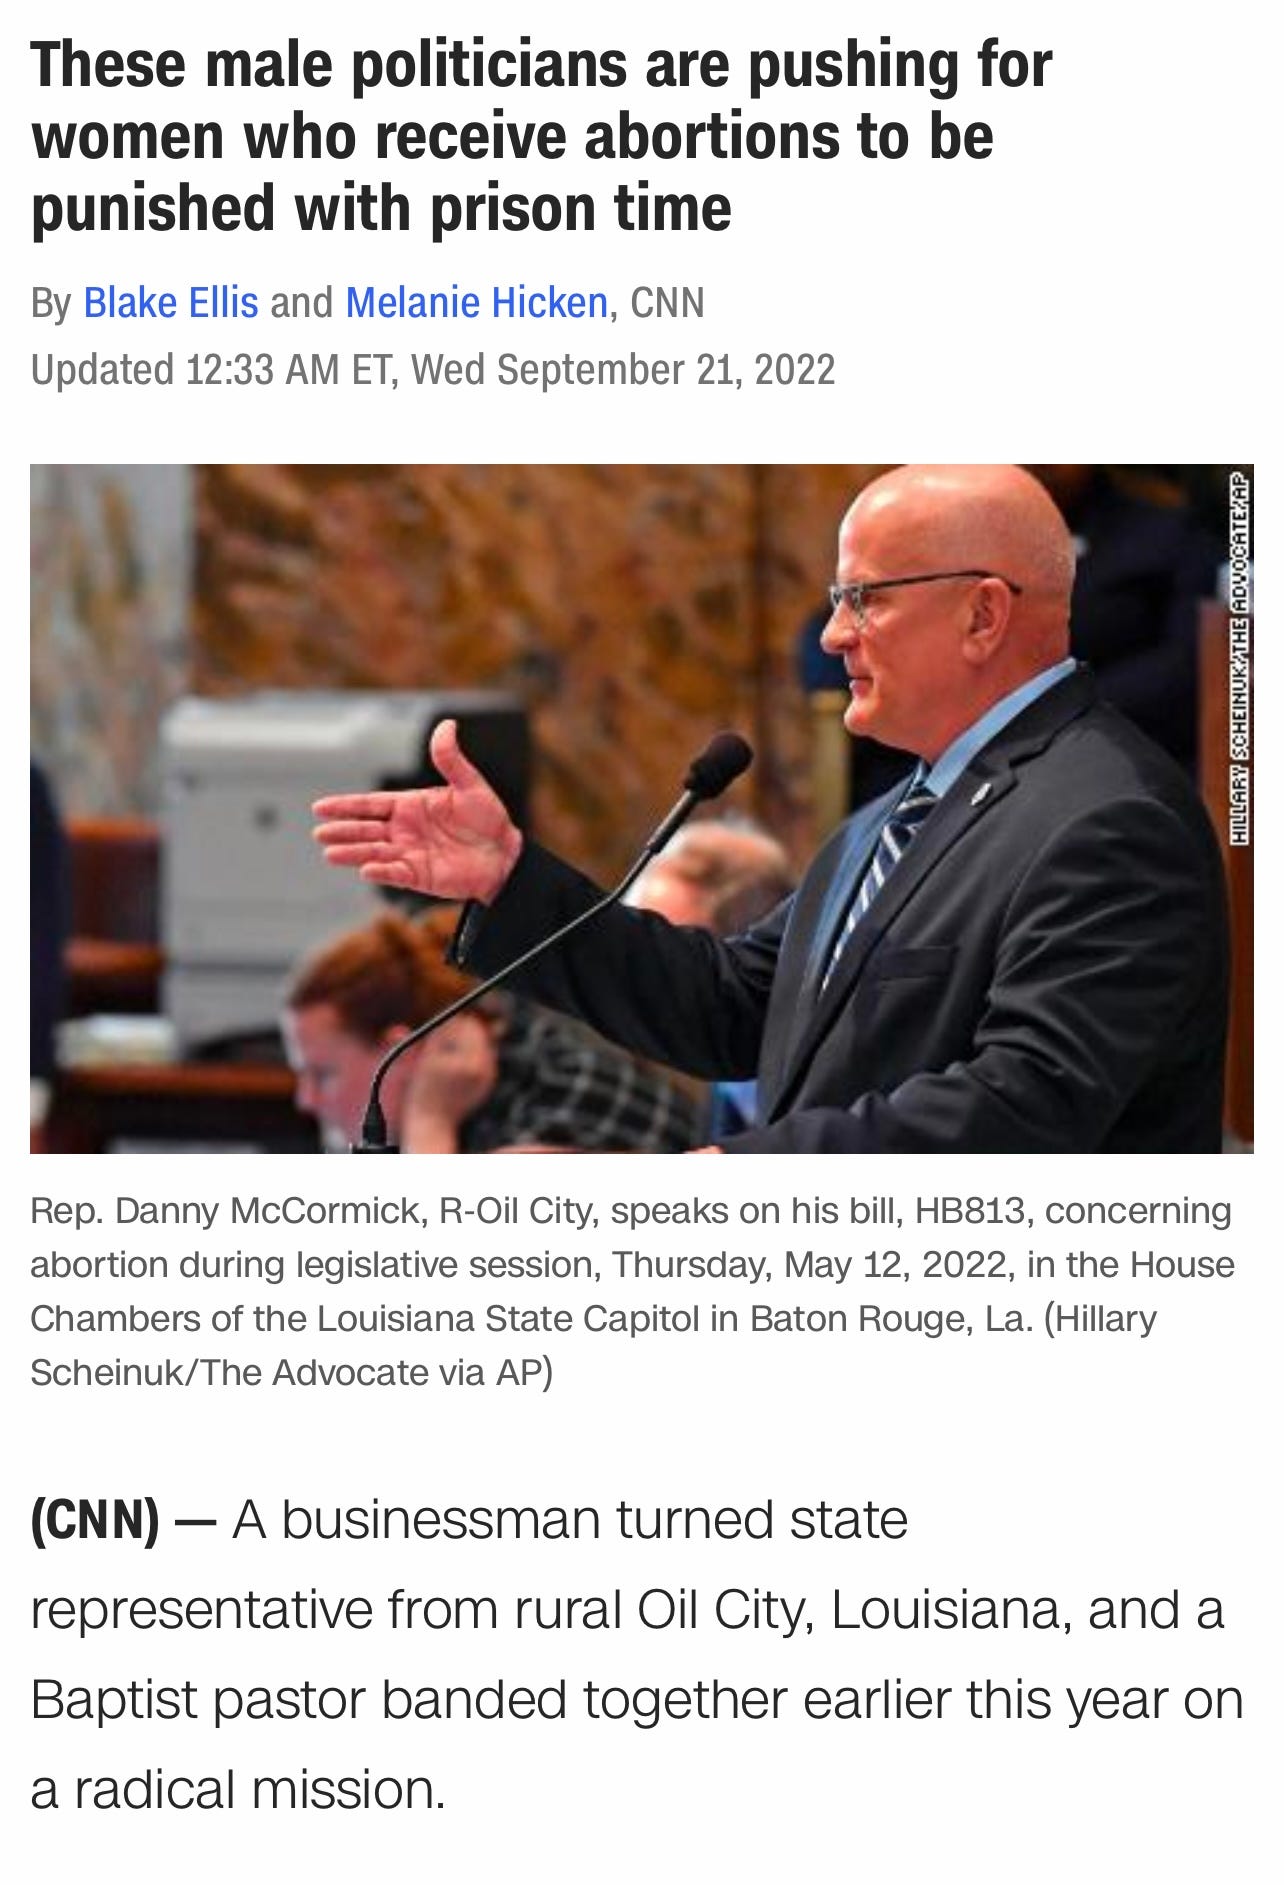
And if my made up law seems like a crazy law, keep in mind, Texas has already defined the standard of care as child abuse. They have asserted a state interest into law-enforcement around a standard of care. Abortion banning states are asserting this law enforcement interest already. If you’re an enemy of the state and you’re being investigated, there’s no reason they can’t review your therapist documentation. Without your knowledge or consent. Because HIPAA expressly allows this.
The Transportation Safety Administration has a notorious track record for stopping nothing dangerous, and every single airplane hijacking has taken place in the context of something they didn’t think about. And yet we all remove our shoes and take off our belts every time we get on a plane. There is no proof this has made us any safer. It’s kabuki. It wastes our time. It wastes our money. It’s worse in healthcare. I once spent three days as an inpatient psychiatric doctor trying to figure out who the hell a patient was. He showed up on the unit, he used a fake name, and we could tell he probably wasn’t Nasir Jones. For those a bit older, this is the full name of the rapper Nas. In this sort of fake story the individual was white, and self-reportedly 21, but looked a lot more like 14. We were really lucky, because he turned out to actually be 15, and we were then able to back-solve who he was and call his family—which would have been a HIPAA violation had he been an adult. Legally, he was a minor, and he was on an adult psychiatric unit, and this meant his parents had a right to make medical decisions.
I can tell the story, because it’s actually not the only time this is happened, it’s happened many times. And even using the fake name of Nasir Jones, that happened three times in one week. Nothing private is revealed here!
This is a broad, sweeping, and unbelievably Orwellian law. To call protected health information protected when what is being authorized is sharing without your knowledge or consent—this is 1984-level wordplay. 1984 was supposed to be a dystopian novel, not the standard of privacy in America.
I Need More of a Call to Action
I asked @CarleneMac how this should end. Her response was:
You need more of a call to action or like a "next time someone tells you they can't do some totally common sense collaborative care thing because "HIPAA" send them this article and remind them that HIPAA is taking your shoes off at the airport while the plane is being highjacked anyways.”
I agree.
—O. Scott Muir, M.D.
Who among us has not accidentally written HIPPA?! It’s also the acronym most frequently chosen by lovers of the word “compliance” in any given context in which they might get to spend seven minutes in heaven together. You know, like at an awkward high school party for junior lexicographers and junior judicial scholars?
Specifically the 12th amendment
I’m looking at you, Bloomberg.
I am looking at you, Texas.
Which could’ve been called disclosable health information any time we goddamn feel like it, but that would’ve given away the scam.
Exception: A group health plan with fewer than 50 participants that is administered solely by the employer that established and maintains the plan is not a covered entity.
Disclosure to the individual (if the information is required for access or accounting of disclosures, the entity MUST disclose to the individual)
Treatment, payment, and healthcare operations
Opportunity to agree or object to the disclosure of PHI
An entity can obtain informal permission by asking the individual outright, or by circumstances that clearly give the individual the opportunity to agree, acquiesce, or object
Incident to an otherwise permitted use and disclosure
Limited dataset for research, public health, or healthcare operations